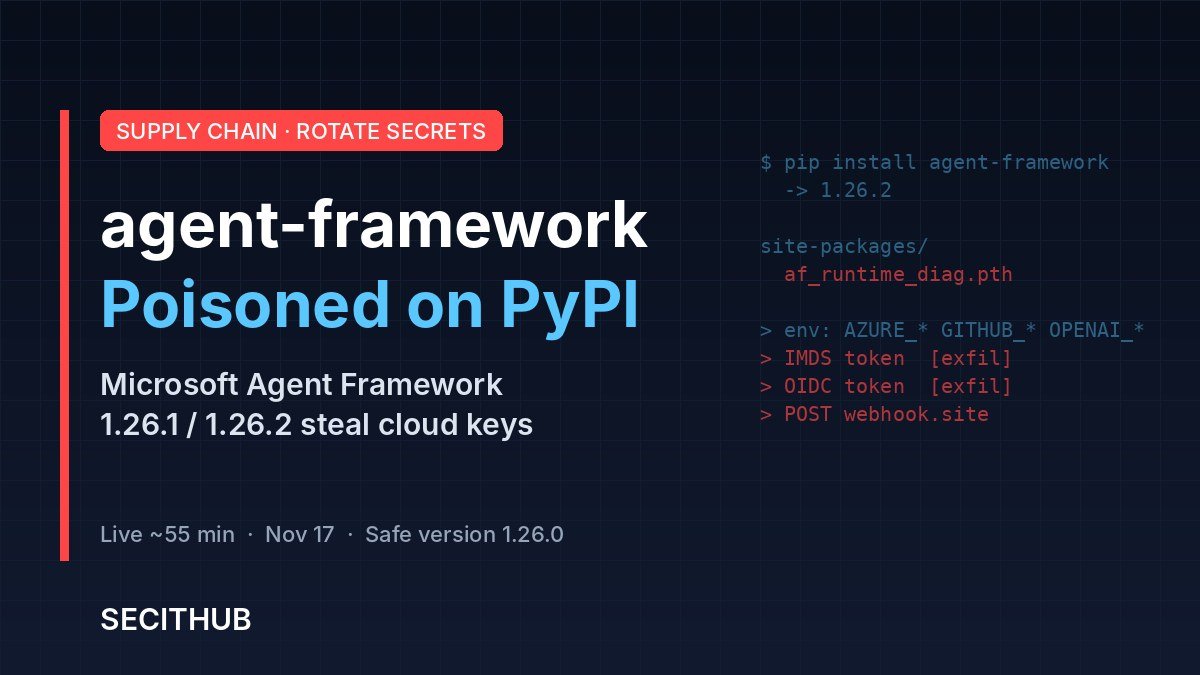
Reading Time: 5 minTwo malicious versions of Microsoft’s agent-framework package hit PyPI for about 55 minutes and ran a credential stealer on every Python start. Here is how it worked, who is exposed and what to rotate now.
Read MoreMicrosoft Agent Framework PyPI Compromise | How a 55-Minute Release Stole Cloud Secrets